Reconstructing the digital crime scene
We treat cyber incidents as investigations, combining digital forensics with document, imagery and identity expertise to establish what actually happened.
Overview
Cyber security incidents rarely exist in isolation. Modern investigations often involve a combination of digital systems, user identity, communications, documents and other forms of evidence that must be interpreted together to understand what has occurred and how it can be proven. Effective response therefore requires more than technical recovery, it requires a forensic approach to reconstructing events across both digital and identity-related evidence sources.
Our Credentials
- Licence
- NSW Security Master Licence 000107811
- Certification
- GIAC GCFE, GCFA
- Clearance
- Security-cleared consultants
Case Study
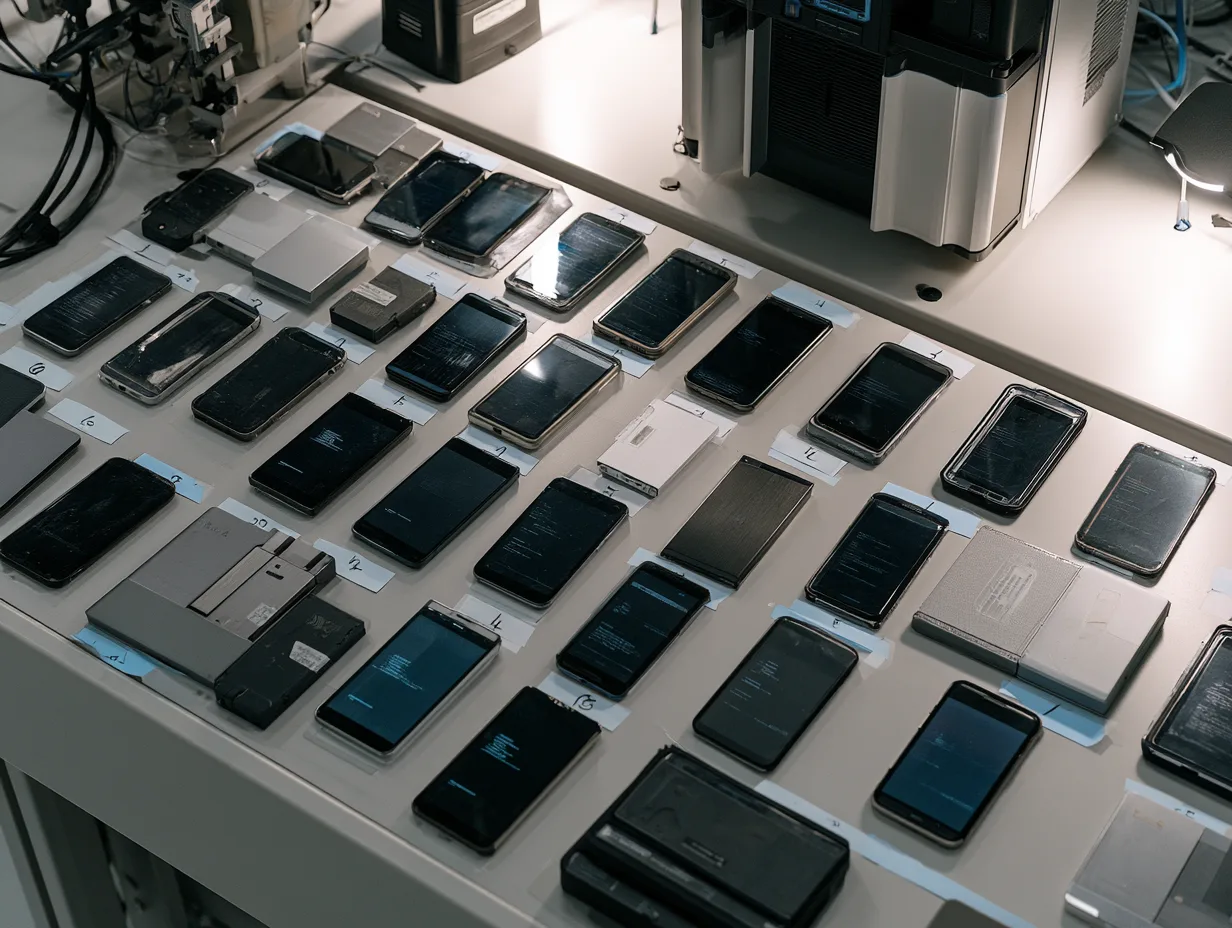
Digital forensic assurance after a major incident
A government agency needed an evidence-based way to assure large volumes of static data before migrating it, including where the source environment may have been compromised. ForenSys designed a file-level assurance model that categorised data by risk and identified indicators of compromise.